Emil Emilov
Projects Skills Exp About Contact Me

I build systems that don't fall over —

and fix the ones that already have.

Not mockups — live systems running today.

Emil Emilov | Systems & Infrastructure

· ·
EE P01
Hotel Terra Europe Brontes

Complete rebuild of a 4-star hotel's marketing and booking site from a static template into a real product: custom navy/gold design system, full BG/EN/TR translation layer, an interactive date-range picker, and a database-driven booking pipeline with email-verified guest submissions. Built a full internal admin panel from scratch — role-based access (Superadmin/Admin/Reception) with a content-approval workflow so front-desk staff can add photos and news posts without publishing unsupervised. Includes real SMTP email notifications, Cloudflare Turnstile bot protection, and per-IP/per-email rate limiting.

Discover ↗
← Back
Hotel Terra Europe Brontes

Complete rebuild of a 4-star hotel's marketing and booking site from a static template into a real product: custom navy/gold design system, full BG/EN/TR translation layer, an interactive date-range picker, and a database-driven booking pipeline with email-verified guest submissions. Built a full internal admin panel from scratch — role-based access (Superadmin/Admin/Reception) with a content-approval workflow so front-desk staff can add photos and news posts without publishing unsupervised. Includes real SMTP email notifications, Cloudflare Turnstile bot protection, and per-IP/per-email rate limiting.

Restaurant section — table reservations, plus Lunch, Dinner and Drinks menus read live from the hotel's POS system, so the head waiter updates the website from the till.
Full i18n system — BG/EN/TR, DB-persisted for logged-in users, cookie-persisted for guests
Role-based admin panel — Dashboard, Customers, Inquiries, Rooms & Spaces, Gallery, News & Events, Admin management
Content-approval workflow — Reception-submitted photos/posts held for admin review before going live
Per-room photo galleries synced from real server folders, with a lightbox viewer
Email verification (double opt-in) for both loyalty accounts and guest bookings
PHP MySQL i18n Admin Panel
EE P02
Hotel Network Infrastructure
ISP 1 PRIMARY ISP 2 MIKROTIK VLAN 1 VLAN 2 VLAN 3 GUEST 9-FLOOR COVERAGE 32 ACCESS POINTS
Hotel Network Infrastructure

Full enterprise network design and deployment for a 9-floor hotel. Built from scratch — planning, hardware selection, installation, and ongoing management.

Discover ↗
← Back
Hotel Network Infrastructure

Full enterprise network design and deployment for a 9-floor hotel. Built from scratch — planning, hardware selection, installation, and ongoing management.

3 ISPs → MikroTik core router (failover + per-subnet load distribution)
32 Access Points across 9 floors (seamless roaming)
Unmanaged Gigabit TP-Link switch distributing most floors off the RB5009 core — floor 4 and the office connect directly to the router instead
5 VLANs — Staff, Guest, and three expandable Systems/IoT segments
Guest and Systems VLANs expandable per floor/zone, DHCP pools scaling to roughly 500 IPs
Captive portal with QR code scanning → instant internet access
MikroTik VLANs OpenWRT Hotspot Captive Portal
EE P03
ARK Platform — ks.vg

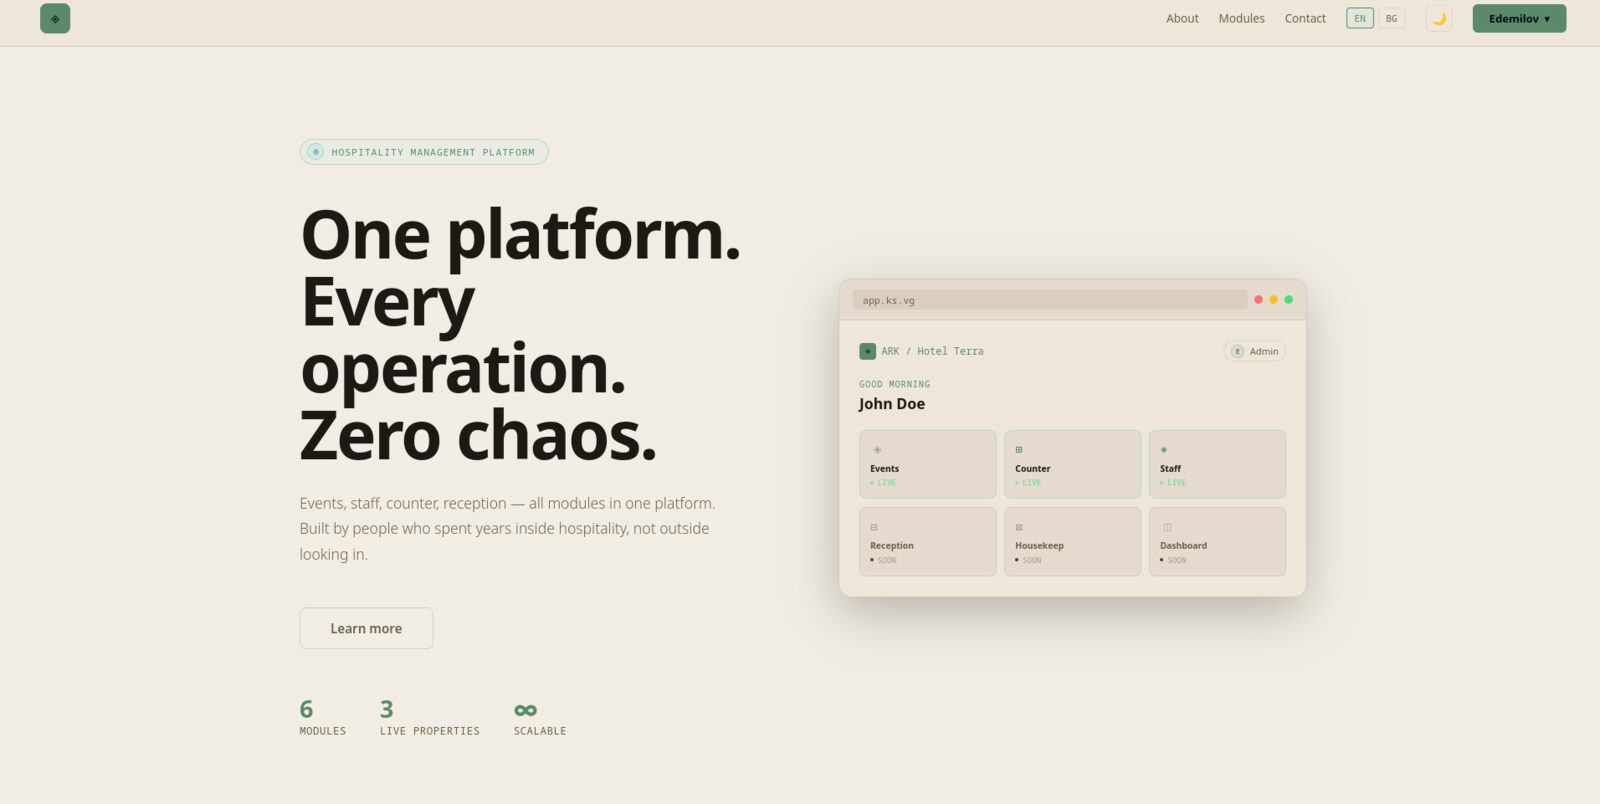
A complete hospitality management platform. Multiple hotels, one login. Each property gets its own modules — Events, Counter POS, Workers, Reception. The interface is available in Bulgarian, English and Turkish. Each business sees only its own data and roles, and staff who work in more than one place switch between them. Each property can connect its own website through revocable API keys. Each module can be sold on its own, with a free trial, usage limits and a paused mode, all enforced on the server, so a client cannot unlock a module from their own side. For support, an administrator can view a business exactly as one of its staff, a role or a customer sees it; the view is look-only, enforced twice on the server (every change is refused and the database connection is read-only), and every view is logged. Client websites run live on their own ks.vg address or on the client's own domain. Orders portal customers can have agreed terms: a discount or fixed prices per product. A client's own web designer can embed the live menu or shop catalogue with two pasted lines; the key works only on the domains the client lists, with daily quotas and rate limits. The platform's move to a rented server is scripted and was rehearsed in three full dry runs, with a cutover and rollback checklist. Staff can sign in on a client's own website through a hidden key press or triple tap, see only the modules their role allows in a white-label left bar, and install the site as a phone app from the client's address, with no app store. An OAuth-style client login (authorization code with PKCE) and a small kit let a client's own site show platform data after sign-in. A rank model lets a person manage only people strictly below their rank. A security pass added login throttling, constant-time password checks, stronger password hashes upgraded at next login, origin checks, secure __Host- cookies and revoke-everyone switches, plus a cookie audit across all sites. Ten website layouts are available, and the application was renamed from ARK to ks.vg with a light default theme. From 31 October to 3 November every client got one predictable address of the form business-name.ks.vg, with a staff-only mode that closes the public site. A tenant-isolation pass closed twelve cross-business reads, and the whole platform moved without a wipe from a home server to a hardened VPS beside the mail server, with a scripted data restore checked by row counts, a tested rollback and 30-minute off-site database pulls. A public brand guide went live in English and Bulgarian. Next, the platform's real screens were ported module by module onto a client's own address through one generic mount, so onboarding a client is configuration rather than code, and a security audit closed cross-business reads in the staff, supply, POS, reception and ticket screens, backed by a two-business end-to-end test of 136 assertions. Five landing-page designs became reusable website templates.

Discover ↗
← Back
ARK Platform — ks.vg

A complete hospitality management platform. Multiple hotels, one login. Each property gets its own modules — Events, Counter POS, Workers, Reception. The interface is available in Bulgarian, English and Turkish. Each business sees only its own data and roles, and staff who work in more than one place switch between them. Each property can connect its own website through revocable API keys. Each module can be sold on its own, with a free trial, usage limits and a paused mode, all enforced on the server, so a client cannot unlock a module from their own side. For support, an administrator can view a business exactly as one of its staff, a role or a customer sees it; the view is look-only, enforced twice on the server (every change is refused and the database connection is read-only), and every view is logged. Client websites run live on their own ks.vg address or on the client's own domain. Orders portal customers can have agreed terms: a discount or fixed prices per product. A client's own web designer can embed the live menu or shop catalogue with two pasted lines; the key works only on the domains the client lists, with daily quotas and rate limits. The platform's move to a rented server is scripted and was rehearsed in three full dry runs, with a cutover and rollback checklist. Staff can sign in on a client's own website through a hidden key press or triple tap, see only the modules their role allows in a white-label left bar, and install the site as a phone app from the client's address, with no app store. An OAuth-style client login (authorization code with PKCE) and a small kit let a client's own site show platform data after sign-in. A rank model lets a person manage only people strictly below their rank. A security pass added login throttling, constant-time password checks, stronger password hashes upgraded at next login, origin checks, secure __Host- cookies and revoke-everyone switches, plus a cookie audit across all sites. Ten website layouts are available, and the application was renamed from ARK to ks.vg with a light default theme. From 31 October to 3 November every client got one predictable address of the form business-name.ks.vg, with a staff-only mode that closes the public site. A tenant-isolation pass closed twelve cross-business reads, and the whole platform moved without a wipe from a home server to a hardened VPS beside the mail server, with a scripted data restore checked by row counts, a tested rollback and 30-minute off-site database pulls. A public brand guide went live in English and Bulgarian. Next, the platform's real screens were ported module by module onto a client's own address through one generic mount, so onboarding a client is configuration rather than code, and a security audit closed cross-business reads in the staff, supply, POS, reception and ticket screens, backed by a two-business end-to-end test of 136 assertions. Five landing-page designs became reusable website templates.

Events — Full event lifecycle, menu planning, kitchen/waiter/client print sheets, allergen tracking, deposit management.
Counter — POS system for hotel bar, coffee shop, restaurant. Tables, orders, fiscal printer integration, end-of-shift reports. Guests can browse the menu and order from a QR code at the table. The head waiter keeps daily Lunch, Dinner and Drinks lists that feed the POS, the table QR, printable menus and the hotel website.
Workers — QR check-in/out, schedule builder, overtime calculation, payroll export.
Menus — One builder for restaurant menus, event packages and client proposals, with variants, per-person pricing and print templates. A menu is applied to an event in one step. Menus print in Bulgarian or English, with optional portion sizes and allergens. Print templates keep a long menu on one page.
Catalogue — Dishes, drinks and ingredients on one screen, with recipes, pack sizes, cost per portion and automatic shopping lists for events. Buy prices per case and per bottle, temporary supplier offers with an end date, price history and stock counts live on one Prices page, so event costing always uses the price actually paid. A dish can appear in several categories, and categories can share one heading on guest-facing menus. English dish descriptions are written from the recipes and appear in print, on the guest QR page and in the website feed.
Orders portal — A B2B ordering portal for any supplier. Customer companies register and are approved by the supplier, see prices and promotions, order for a delivery date, and can change or cancel until a cutoff time. Each customer has an account (prepaid balance, credit with a limit, or cash) with a full statement. The supplier checks every order, removes, replaces or adds items, and the customer sees exactly what changed. Notification emails go through an outbox with retry. Tested end to end; in trial on a pilot business.
PHP PostgreSQL Multi-tenant SSO Claude
EE P04
Proxmox Homelab
Proxmox Homelab
Proxmox Homelab

Full self-hosted infrastructure running on a single Proxmox VE node. AMD Ryzen 5 5500GT, 16GB RAM, ~20TB across 4 ZFS pools. Also the proving ground for self-hosted AI infrastructure: a personal AI agent (OpenClaw), local LLM inference via Ollama on a dedicated GPU workstation with a RAG pipeline over a personal knowledge base, and an agentic dispatcher routing bash/coding tasks to local models. Recently audited the full local-model roster with real tool-calling tests (not just load-success checks) across three independent integration paths, pruned it down to a single verified-reliable model, and live-confirmed the entire chain end-to-end after reconfiguring every dependent tool. Patch levels are checked across the whole fleet: for the PHP 8.4.26 security release, every host running PHP (Nextcloud, the application containers and the standby site) was verified, and the one host still behind (the mail VPS) was upgraded to PHP 8.5.12 and re-verified. An unattended AI job runner lives in its own unprivileged container: it sees only one folder of my notes vault through a dedicated Nextcloud user, runs Claude Code jobs from queued job notes with a tool allow-list and time and turn limits, writes its results back and reports every run by Telegram. Its first job produced the school reference cards for pi.gd (13 subjects, about 770 topics, 28 runs); when its sync stalled I traced it to stale Redis file locks (423 Locked) and cleared them.

Discover ↗
← Back
Proxmox Homelab

Full self-hosted infrastructure running on a single Proxmox VE node. AMD Ryzen 5 5500GT, 16GB RAM, ~20TB across 4 ZFS pools. Also the proving ground for self-hosted AI infrastructure: a personal AI agent (OpenClaw), local LLM inference via Ollama on a dedicated GPU workstation with a RAG pipeline over a personal knowledge base, and an agentic dispatcher routing bash/coding tasks to local models. Recently audited the full local-model roster with real tool-calling tests (not just load-success checks) across three independent integration paths, pruned it down to a single verified-reliable model, and live-confirmed the entire chain end-to-end after reconfiguring every dependent tool. Patch levels are checked across the whole fleet: for the PHP 8.4.26 security release, every host running PHP (Nextcloud, the application containers and the standby site) was verified, and the one host still behind (the mail VPS) was upgraded to PHP 8.5.12 and re-verified. An unattended AI job runner lives in its own unprivileged container: it sees only one folder of my notes vault through a dedicated Nextcloud user, runs Claude Code jobs from queued job notes with a tool allow-list and time and turn limits, writes its results back and reports every run by Telegram. Its first job produced the school reference cards for pi.gd (13 subjects, about 770 topics, 28 runs); when its sync stalled I traced it to stale Redis file locks (423 Locked) and cleared them.

Nextcloud — Family file sync, calendar, contacts
Immich — Photo library with ML face recognition
Jellyfin — Media server (1.4TB TV, 217GB movies, 406GB music)
Vaultwarden — Bitwarden-compatible password manager
Gitea — Self-hosted Git
Pi-hole — Network-wide DNS ad blocker
Proxmox ZFS LXC Self-hosted Docker Ollama LLM
EE P05
Cloudflare Zero-Trust Stack

Every public-facing service runs through Cloudflare Tunnel — no ports open on the firewall. DNS managed via Cloudflare, wildcard certificates, DDoS protection built in. Administrative/management access on the router side gets the same zero-trust treatment: no exposed management ports, and every edge router is actively hardened and audited, not just configured once.

Discover ↗
← Back
Cloudflare Zero-Trust Stack

Every public-facing service runs through Cloudflare Tunnel — no ports open on the firewall. DNS managed via Cloudflare, wildcard certificates, DDoS protection built in. Administrative/management access on the router side gets the same zero-trust treatment: no exposed management ports, and every edge router is actively hardened and audited, not just configured once.

cloudflared daemon in LXC → outbound tunnel to Cloudflare edge
NPM (nginx Proxy Manager) → routes by hostname
Zero inbound firewall rules needed
Wildcard SSL — *.ks.vg, *.edemilov.com, *.pi.gd, *.mr.photos
Cloudflare WAF + DDoS mitigation
Multiple domains: ks.vg · edemilov.com · pi.gd · mr.photos
Cloudflare Zero-trust nginx SSL Tunnel
EE P06
WalletPi — Personal Finance Tracker

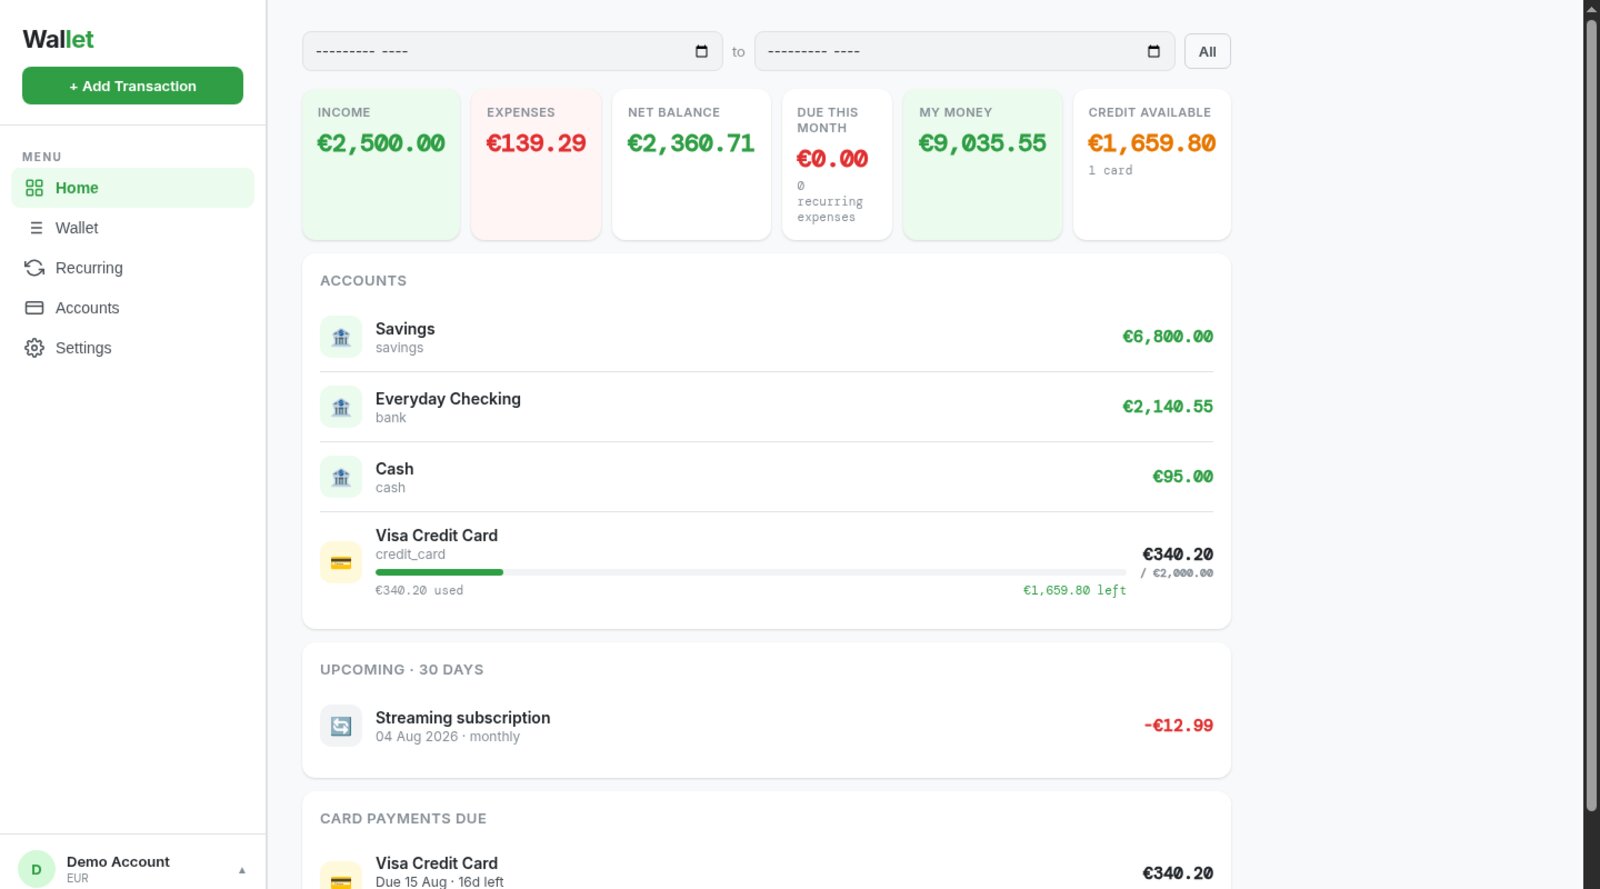
A full-featured multi-user personal finance tracker — accounts, categorized transactions, recurring bills, and a dashboard that actually separates real cash from available credit. Manual entry by design, so it needs no bank API connections or PCI-level security surface.

Discover ↗
← Back
WalletPi — Personal Finance Tracker

A full-featured multi-user personal finance tracker — accounts, categorized transactions, recurring bills, and a dashboard that actually separates real cash from available credit. Manual entry by design, so it needs no bank API connections or PCI-level security surface.

Multi-account tracking — bank, cash, savings, credit card, and crypto accounts side by side
Credit card intelligence — limit, due date, minimum payment, and a live utilization bar, not just a balance
Recurring bills — subscriptions, leases, salary, on any schedule from daily to yearly, auto-generating transactions
Dashboard that separates "my money" from available credit, plus a 30-day upcoming view and card-payments-due panel
Multi-user with an admin-approval flow — first account becomes admin, everyone after needs sign-off before they can log in
Full EN/BG/TR interface
EE P07
Personal Notes
Personal Notes
Personal Notes

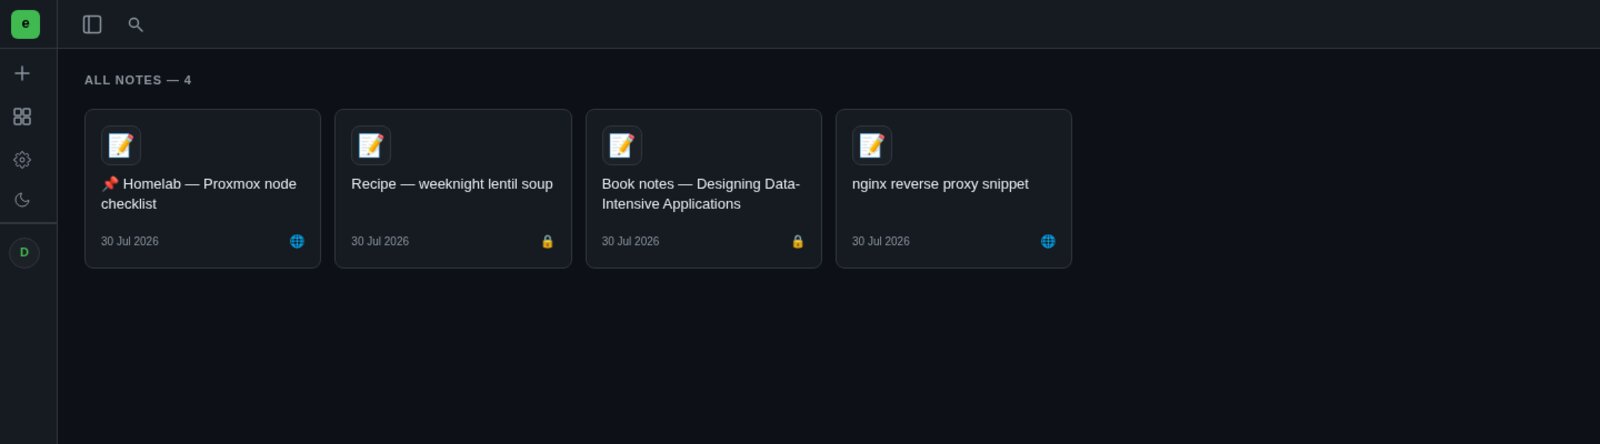
A private, invite-only space for markdown notes, code snippets, and technical references — rewritten from a live Node.js/Express app to PHP 8.4 with zero data loss. Each note is public or private, taggable, and searchable, with an admin panel for issuing invite codes instead of open registration.

Discover ↗
← Back
Personal Notes

A private, invite-only space for markdown notes, code snippets, and technical references — rewritten from a live Node.js/Express app to PHP 8.4 with zero data loss. Each note is public or private, taggable, and searchable, with an admin panel for issuing invite codes instead of open registration.

Rewrote a live Node.js/Express app to PHP 8.4 in place, migrating the PostgreSQL schema (users, notes, tags, attachments, invites) with zero data loss
Per-note public/private visibility, so individual references can be shared without opening the whole notebook
Full tag system with filtering — 40+ tags across a real, actively-used note collection
Invite-only registration — admin generates and revokes invite codes instead of open sign-up
Markdown rendering with code-block support, built for technical reference notes and snippets
php - sql
EE P08
pi.gd — Personal web platform with one login

Designed and built, from a written spec and a 14-task plan, the site behind pi.gd: a bilingual (Bulgarian and English) platform with a Tech section, a Tools section, a blog run by a family member as editor, and school reference pages for my children. Plain PHP 8.4 and PostgreSQL with no framework and no CDN, live since 14 October 2026.

Discover ↗
← Back
pi.gd — Personal web platform with one login

Designed and built, from a written spec and a 14-task plan, the site behind pi.gd: a bilingual (Bulgarian and English) platform with a Tech section, a Tools section, a blog run by a family member as editor, and school reference pages for my children. Plain PHP 8.4 and PostgreSQL with no framework and no CDN, live since 14 October 2026.

Tech: Linux distro picks with a nightly DistroWatch top 10
Tools: the CV Builder, a finance tracker (by invitation) and a calculator, all on one login
Ay's Corner: a blog with hashtags and full-text search that also works in Cyrillic
School: maths and physics cards for grades 6 to 9 with step-by-step worked examples
Accounts with verified email and five levels (user, superuser, moderator, editor, admin) enforced on the server; staff log in with two-factor codes, encrypted secrets, recovery codes and replay protection
One login for every tool: each tool is a module that is either open or restricted. For a restricted tool a user asks for access and a moderator approves it, or the user enters a one-time invite code that is stored hashed, valid for 14 days and works once
PHP 8.4 PostgreSQL Security Two-factor login Cloudflare
EE P09
hyprevo — Hyprland+DMS Installer

A public, Arch-only (pacman, no AUR) one-command installer that sets up a full Hyprland + Quickshell/DMS desktop environment from scratch. Modeled on Proxmox's community helper-scripts: an interactive whiptail picker (terminal, file manager, mail client, cloud sync as single-choice radiolists, plus an independent checklist for extras) instead of a fixed opinionated bundle, with picks wired into a separate extras.conf so the base hyprland.conf stays clean. Built test-first with bats unit tests and shellcheck before any live run, then hardened through a second person live-installing it in a fresh VM, which surfaced real bugs invisible from local testing alone.

Discover ↗
← Back
hyprevo — Hyprland+DMS Installer

A public, Arch-only (pacman, no AUR) one-command installer that sets up a full Hyprland + Quickshell/DMS desktop environment from scratch. Modeled on Proxmox's community helper-scripts: an interactive whiptail picker (terminal, file manager, mail client, cloud sync as single-choice radiolists, plus an independent checklist for extras) instead of a fixed opinionated bundle, with picks wired into a separate extras.conf so the base hyprland.conf stays clean. Built test-first with bats unit tests and shellcheck before any live run, then hardened through a second person live-installing it in a fresh VM, which surfaced real bugs invisible from local testing alone.

Terminal — Konsole / Terminator / Kitty / Alacritty
File manager
Mail client
Cloud sync
Extras — Telegram, screen capture, Bitwarden (independent toggles)
Bash Hyprland Wayland Quickshell/DMS bats shellcheck
EE P10
Self-Hosted Mail Server — pi.gd / ks.vg / edemilov.com

Built and hardened a full self-hosted mail platform (HestiaCP: Exim, Dovecot, ClamAV, SpamAssassin, DKIM/SPF/DMARC, Roundcube webmail) on a dedicated VPS, replacing a forward-only Cloudflare Email Routing setup with real send and receive for all 3 domains and 9 live mailboxes.

Discover ↗
← Back
Self-Hosted Mail Server — pi.gd / ks.vg / edemilov.com

Built and hardened a full self-hosted mail platform (HestiaCP: Exim, Dovecot, ClamAV, SpamAssassin, DKIM/SPF/DMARC, Roundcube webmail) on a dedicated VPS, replacing a forward-only Cloudflare Email Routing setup with real send and receive for all 3 domains and 9 live mailboxes.

Correctly wired the full deliverability chain — PTR/HELO/hostname identity, DKIM, SPF, DMARC — matched across mail server and DNS
Verified end-to-end with real Gmail round-trip tests in both directions across all 3 domains, confirmed landing in the inbox (not spam) on a zero-reputation fresh IP
Ran a full security pass: own audit plus an independent DeepSeek second opinion fed the real config
Found and closed a live SSH password-auth bypass around existing passwordless-sudo hardening
Found and closed FTP cleartext logins for a sudo-capable system account, and unnecessary BIND public exposure
Rotated every panel/mailbox/system credential
HestiaCP Exim Dovecot DKIM/SPF/DMARC Roundcube Tailscale
EE P11
Media Automation Pipeline — Sonarr/Radarr/qBittorrent

Diagnosed a subtle, silent access-control misconfiguration that had disabled every automated download across three services (Sonarr, Radarr, Lidarr) for two full days with no visible error — a well-intentioned but mistaken tag-based routing scheme had tagged both the indexers and the download clients, which independently gate on the content's own tags rather than on each other, so nothing was ever tagged and every indexer/client silently went unusable.

Discover ↗
← Back
Media Automation Pipeline — Sonarr/Radarr/qBittorrent

Diagnosed a subtle, silent access-control misconfiguration that had disabled every automated download across three services (Sonarr, Radarr, Lidarr) for two full days with no visible error — a well-intentioned but mistaken tag-based routing scheme had tagged both the indexers and the download clients, which independently gate on the content's own tags rather than on each other, so nothing was ever tagged and every indexer/client silently went unusable.

Traced from a vague symptom (playback issues on some downloaded files) through a quality-profile misconfiguration — most of the library was on an unrestricted profile instead of the intended capped one, letting oversized/incompatible releases through
Found the real root cause via direct application log inspection ("0 active indexers" on every search), not guesswork — confirmed empirically before touching any config
Fixed the tag-based routing mistake across all three apps (Sonarr, Radarr, Lidarr), restoring normal automated search and download immediately
Replaced the original broken automation idea with a safer systemd-timer-based cleanup job that only ever acts on state the download client has already independently confirmed is safe to reclaim, rather than guessing at source-based rules
Verified the fix end-to-end with real grabs completing successfully, not just config validation
Sonarr Radarr Lidarr qBittorrent systemd Debugging
EE P12
mr.photos — Kids' Art Gallery

Designed, built and deployed a public online museum for children's drawings and paintings: anyone can browse, registered users upload, and every picture is approved by a moderator before it is shown. Plain PHP 8.4 and PostgreSQL with no framework, a Bulgarian/English interface, and a landing page where gold-framed pictures orbit an empty, lit centre like Saturn's rings.

Discover ↗
← Back
mr.photos — Kids' Art Gallery

Designed, built and deployed a public online museum for children's drawings and paintings: anyone can browse, registered users upload, and every picture is approved by a moderator before it is shown. Plain PHP 8.4 and PostgreSQL with no framework, a Bulgarian/English interface, and a landing page where gold-framed pictures orbit an empty, lit centre like Saturn's rings.

Went from idea to written spec to a 14-task implementation plan, then built it task by task with a fresh AI agent per task and an independent code review after every task — 180 automated tests
Accounts with mandatory email verification, password reset and three roles (user, moderator, admin); one moderation queue for pictures and comments, a trust rule that lets proven commenters skip the queue, an email digest for moderators, and nothing ever hard-deleted
Child safety and privacy first: uploads are re-encoded to strip EXIF/GPS location data, unapproved pictures return 404 to everyone except their owner and moderators, public placards show only a first name and age, and parents can withdraw their child's picture at any time
A final whole-codebase security review found real problems before launch — out-of-memory risk from parallel large uploads (image decoding serialised with a lock), an open redirect through tab characters, sessions surviving a password reset, and a missing mail timeout — all fixed and re-reviewed
Deployed to its own Proxmox container behind Cloudflare Tunnel, with outgoing mail DKIM/SPF/DMARC-aligned through the self-hosted mail server, and verified with a 34-step live acceptance run using real email
PHP 8.4 PostgreSQL Security i18n Proxmox Cloudflare Tunnel
EE P13
CV Builder — pi.gd/cv

Designed and built a public CV-builder feature from scratch on the site's own plain PHP 8/PostgreSQL stack, with no framework: a card-gallery landing page, a multi-step wizard (about, experience, education, skills, languages, summary), a clean print-ready view, and, since October 2026, ownership through the shared pi.gd account (at first account-free, with a cookie and an email magic link for recovery).

Discover ↗
← Back
CV Builder — pi.gd/cv

Designed and built a public CV-builder feature from scratch on the site's own plain PHP 8/PostgreSQL stack, with no framework: a card-gallery landing page, a multi-step wizard (about, experience, education, skills, languages, summary), a clean print-ready view, and, since October 2026, ownership through the shared pi.gd account (at first account-free, with a cookie and an email magic link for recovery).

Built spec-first: design spec, then an implementation plan, then subagent-driven development with an independent code review and fix loop after each task
Share links and edit rights are separate secrets, so a shared view link can never grant edit access; the recovery flow answers identically whether or not an email matches, so it cannot be used to find out who has a CV
The final whole-branch review caught five real defects before users did — a broken photo upload, a dead Save button, a wrong claim-email link, a silently dropped email field and a swallowed mail error
The fix for those then broke the wizard itself (a checkValidity() call on a plain div) — caught only because the re-review clicked through the page in a real browser instead of relying on curl checks
Added five selectable print-ready A4 designs with a thumbnail picker and a live design switcher, fixed stale CSS caused by Cloudflare edge caching with mtime-based cache-busting, and re-themed the admin panel from dark to a light pastel palette
Moved onto the shared pi.gd login: CVs now belong to the user's account, a CV made earlier with the cookie or email link moves into the account the first time its holder signs in, and guests only see three example CVs of invented people, never a real person's CV
PHP 8 PostgreSQL Print CSS Security Cloudflare
EE P14
Legacy System Virtualisation (P2V)

Migrating the hotel's core operational software — a property-management system and two point-of-sale/restaurant systems — off ageing physical hardware onto Proxmox virtual machines, without interrupting the live systems the hotel runs on every day.

Discover ↗
← Back
Legacy System Virtualisation (P2V)

Migrating the hotel's core operational software — a property-management system and two point-of-sale/restaurant systems — off ageing physical hardware onto Proxmox virtual machines, without interrupting the live systems the hotel runs on every day.

Standard vssadmin shadow copies turned out to be unsupported on the source machine's Windows edition; engineered an alternative through the WMI Win32_ShadowCopy.Create API under a SYSTEM scheduled task — the same mechanism commercial backup tools use — for a clean copy of in-use databases with zero service interruption
Completed the full source backup, including a 91.8 GB VHDX image of the C: drive pulled over the hotel LAN, and identified three USB licence dongles that will need passthrough in the target VM
Before any restore, found the test VM's 931 GB thin disk sitting on a 348 GB thin pool — 2.7× over-committed, enough to freeze every guest on the host — and recovered headroom with a second LVM-thin pool, byte-verified data moves and fstrim (66% → 34% used)
Found the host's uplink capped at 100 Mbit with 30–40% packet loss by an in-line extender; replaced it with a repurposed MikroTik router set up as a pure Layer-2 switch, giving 1 Gbit with 0% loss
The faster link exposed a known Intel e1000e "Hardware Unit Hang"; recovered the host remotely by bouncing its switch port, then fixed it permanently by disabling TSO/GSO/GRO offloads in the host's network config
Proxmox LVM-thin Windows VSS/WMI MikroTik Networking
EE P15
Security Monitoring & Honeypot

Central security visibility for a homelab, a hotel network and a public mail server. Every server and router sends its logs to one place, alerts arrive on Telegram, known attackers are blocked automatically, and a honeypot records what attackers do once they think they are in.

Discover ↗
← Back
Security Monitoring & Honeypot

Central security visibility for a homelab, a hotel network and a public mail server. Every server and router sends its logs to one place, alerts arrive on Telegram, known attackers are blocked automatically, and a honeypot records what attackers do once they think they are in.

Logs from two Proxmox hosts, 18 containers, a mail server and two MikroTik routers are collected in Loki and kept for 30 days. RouterOS syslog over TCP lacks the trailing newline that Promtail needs, so the routers send UDP through rsyslog relays
Fourteen Grafana alert rules report to Telegram: bursts of failed logins, router login failures and configuration changes, logins from unknown devices, log sources that go silent, touches on the decoy servers and automatic login bans. The rules were tuned after the first day so that only actionable alerts fire
CrowdSec on the reverse proxy: the websites sit behind a Cloudflare Tunnel, so the proxy was configured to trust the real client IP address, and bans are synced into an nginx deny list. Tested end to end with a simulated scanner
CrowdSec on the mail server with an nftables bouncer in its own tables, leaving the control panel's own firewall untouched, plus a custom parser for its Dovecot log format
A Cowrie SSH honeypot answers on port 22 of the mail server, while real SSH runs on another port and outbound traffic is blocked for the honeypot user. It logged more than 500 attacker IP addresses and about 34,000 sessions in the first three days
Internal decoys: on the hotel and the home network an OpenCanary container poses as a NAS with SSH, FTP, telnet and a web login. Nobody has a reason to touch it, so any touch raises an alert naming the device. Each MikroTik router passes attempts on its own FTP and telnet ports to the decoy and logs the device's IP and MAC address. Built the same afternoon an unknown laptop tried anonymous FTP on the hotel router
Loki Grafana CrowdSec Cowrie OpenCanary fail2ban MikroTik
EE P16
Automatic Site Failover: Home to Off-Site Standby

A power cut at home took every public website and the password manager offline, and no copy of the data existed anywhere else. Now a standby container at a second site keeps a copy that is at most two minutes old, takes over by itself when the home server disappears, and returns everything, including what was written in the meantime, when the home server is back.

Discover ↗
← Back
Automatic Site Failover: Home to Off-Site Standby

A power cut at home took every public website and the password manager offline, and no copy of the data existed anywhere else. Now a standby container at a second site keeps a copy that is at most two minutes old, takes over by itself when the home server disappears, and returns everything, including what was written in the meantime, when the home server is back.

The home Proxmox host sends database dumps (PostgreSQL and MariaDB), site files, uploads, nginx and PHP settings and the password manager's database to the standby every two minutes, using a key that can only write into one folder. The standby restores only what changed and keeps the last good copy if a restore fails
No DNS change during a takeover: the standby runs a second connector for the same Cloudflare Tunnel, normally stopped. A watchdog starts it only when Cloudflare itself reports for three minutes that the tunnel has no connector, which also proves that the standby's own internet connection works
Protection against both sites serving at the same time: the home connector no longer starts by itself. A gate service opens it only when the standby is idle, and stops it after two minutes without a connection to Cloudflare, before the standby would take over
Automatic return: when the home server is back, it asks the standby to stop, restores only the databases that differ, fetches only the files written during the outage, and saves every replaced copy first
Proven with real outage tests on the live websites: the standby took over 2 minutes 39 seconds after the home connector stopped, the return took about 40 seconds, and test records written on the standby arrived at home. The first test exposed a mistake: the watchdog was watching an address that Cloudflare redirects by itself, so it never saw the outage. It was fixed and tested again within the hour
Telegram messages on takeover, on return and on errors are sent from the second site, because the monitoring system itself runs on the home server
Proxmox Cloudflare Tunnel PostgreSQL High availability Bash systemd
EE P17
External Security Assessment — VPS/VDS Hosting Platform

Two rounds of an authorized security assessment of a friend's live VPS/VDS reseller platform (a Paymenter-based client panel plus a provisioned test VPS), end to end, each delivered as a full written report.

Discover ↗
← Back
External Security Assessment — VPS/VDS Hosting Platform

Two rounds of an authorized security assessment of a friend's live VPS/VDS reseller platform (a Paymenter-based client panel plus a provisioned test VPS), end to end, each delivered as a full written report.

Round 1: systematic coverage of the checkout/payment flow, XSS across three separate rendering surfaces, IDOR checks across servers/tickets/invoices, account security, file-upload handling and the full VPS lifecycle, each verified against real system state rather than trusted from the admin panel
Identified the platform from its own telemetry and tested directly against its known CVE history: a checkout-parameter price/plan injection and a critical ticket-attachment arbitrary-file-upload RCE class, both confirmed already patched
Found and root-caused one real bug: a VPS restart action was silently regenerating SSH host keys and discarding a customer's hostname customization, traced from host-key timestamps and cloud-init logs to the platform pushing hostname changes through to the hypervisor's VM name; fixed by the owner the same day
Round 2: subdomain enumeration, exposed source-control/environment files, CORS policy, SPF/DKIM/DMARC email authentication, Laravel debug-route exposure, a specific CVE check against a payment-webhook SSRF class, and login rate-limiting
Login rate-limiting tested live against the real login form in a browser rather than by replaying raw requests, since it runs through a JavaScript framework rather than a plain form target; confirmed an invisible bot check and the framework's own throttling both active together
One further low-severity finding (a publicly readable but harmless configuration file) and a recommendation to tighten the domain's email-authentication posture, relevant to a hosting brand's own phishing exposure
Security Pentest Web App Testing
EE S01
Networking
Networking
Networking

Runs network operations for a full hotel property day to day, then mirrors the same patterns at home to keep the muscle memory sharp.

Discover ↗
← Back
Networking

Runs network operations for a full hotel property day to day, then mirrors the same patterns at home to keep the muscle memory sharp.

32 access points across a live hotel site, MikroTik RB5009 as core router
Triple-ISP failover with automatic MikroTik-side switchover and per-subnet load distribution
5 VLANs — staff/management, guest, and expandable systems/IoT segments, DHCP scaling to roughly 500 IPs
DNS/DHCP via PiHole, home lab as a testbed before touching production
RouterOS RAW-table DDoS/ICMP rate-limiting hardening across edge routers
TCP/IP VLANs MikroTik OpenWRT Dual-ISP DNS/DHCP Hotspot
EE S02
Security
Security
Security

Inbound-closed by default — every remote path goes through an explicit tunnel or mesh, never an open port.

Discover ↗
← Back
Security

Inbound-closed by default — every remote path goes through an explicit tunnel or mesh, never an open port.

Tailscale mesh for all admin access, zero exposed management ports
Cloudflare Tunnel fronts every public-facing service instead of port-forwarding
RouterOS RAW-table DDoS/perimeter hardening on every edge router — closed gaps like unrestricted WAN ICMP and unscoped management-service ACLs
Diagnosed and fixed a live Tailscale routing misconfiguration causing source-IP masking that had locked out legitimate SSH access
Self-hosted Vaultwarden for credential management, 2FA everywhere it is supported
Working a structured cert path: Security+ → CySA+ → GCFE/GCFA
Firewall Tailscale VPN Cloudflare Tunnel SSL/TLS pf Zero-trust
EE S03
Virtualisation
Virtualisation
Virtualisation

Runs a real multi-tenant Proxmox host at home the same way you would run one in a datacenter — isolated per service, backed up, monitored.

Discover ↗
← Back
Virtualisation

Runs a real multi-tenant Proxmox host at home the same way you would run one in a datacenter — isolated per service, backed up, monitored.

15+ LXC containers on Proxmox VE, one service per container
Migrated three live production sites off a shared web+DB pair onto dedicated per-domain containers with zero downtime
Docker/Compose layered on top where it fits better than native LXC
Automated daily/weekly backups (PBS) across tiered ZFS storage
Proxmox VE LXC KVM Docker Compose Portainer PBS
EE S04
Storage
Storage
Storage

ZFS end to end — tiered pools, scrubbed and verified, sized for headroom rather than filled to the edge.

Discover ↗
← Back
Storage

ZFS end to end — tiered pools, scrubbed and verified, sized for headroom rather than filled to the edge.

Four ZFS pools spanning ~18TB (HDD bulk + NVMe fast tier), all scrubbed clean
Samba/CIFS shares for the whole household plus dedicated dev mounts
Snapshot-based backup strategy, daily and weekly rotation
NVMe reserved for live app/container disks, HDD for media and cold backups
ZFS Btrfs NFS Samba/CIFS Snapshots Tiered pools
EE S05
Operating Systems
Operating Systems
Operating Systems

Genuinely does not have a favorite distro — picks whichever one fits the job and stays current on the rest by actually running them.

Discover ↗
← Back
Operating Systems

Genuinely does not have a favorite distro — picks whichever one fits the job and stays current on the rest by actually running them.

Arch/CachyOS as daily driver, Debian underneath Proxmox and most production containers
RHEL/Rocky and Ubuntu Server for anything expecting an enterprise-standard base
Windows Server & Active Directory from hands-on hotel IT administration
FreeBSD and legacy Novell/eDirectory exposure — comfortable outside the Linux-only comfort zone
Arch/CachyOS Debian RHEL/Rocky Ubuntu Server Windows Server & AD FreeBSD Novell legacy systems
EE S06
Development
Development
Development

Ships and maintains real production PHP/Python apps end to end — schema, backend, deploy, and the bug report that comes after.

Discover ↗
← Back
Development

Ships and maintains real production PHP/Python apps end to end — schema, backend, deploy, and the bug report that comes after.

Built the ARK hotel platform (events, staff, reception, kitchen — one codebase, several subdomains)
Rewrote a live Node.js/Express app to PHP 8.4 with zero data loss
PostgreSQL and MariaDB schema design, REST APIs, admin tooling
Comfortable across the full path from a bare VM to a deployed, monitored app
PHP 8.4 Python Bash PostgreSQL MariaDB REST APIs HTML/CSS
EE S07
AI Engineering
AI Engineering
AI Engineering

Treats LLMs as another service to architect around, not a black box to prompt and hope.

Discover ↗
← Back
AI Engineering

Treats LLMs as another service to architect around, not a black box to prompt and hope.

Designs RAG pipelines end to end — embedding model choice, indexing, retrieval, generation
Wires agentic tool-use via MCP so models can call real infrastructure, not just chat
Works daily with the Claude API and multi-agent workflows on production codebases
Thinks in context windows, tool schemas, and failure modes — not just prompts
LLM app design RAG pipelines Prompt & context engineering Agentic tool-use (MCP) Claude API integration Multi-model orchestration
EE S08
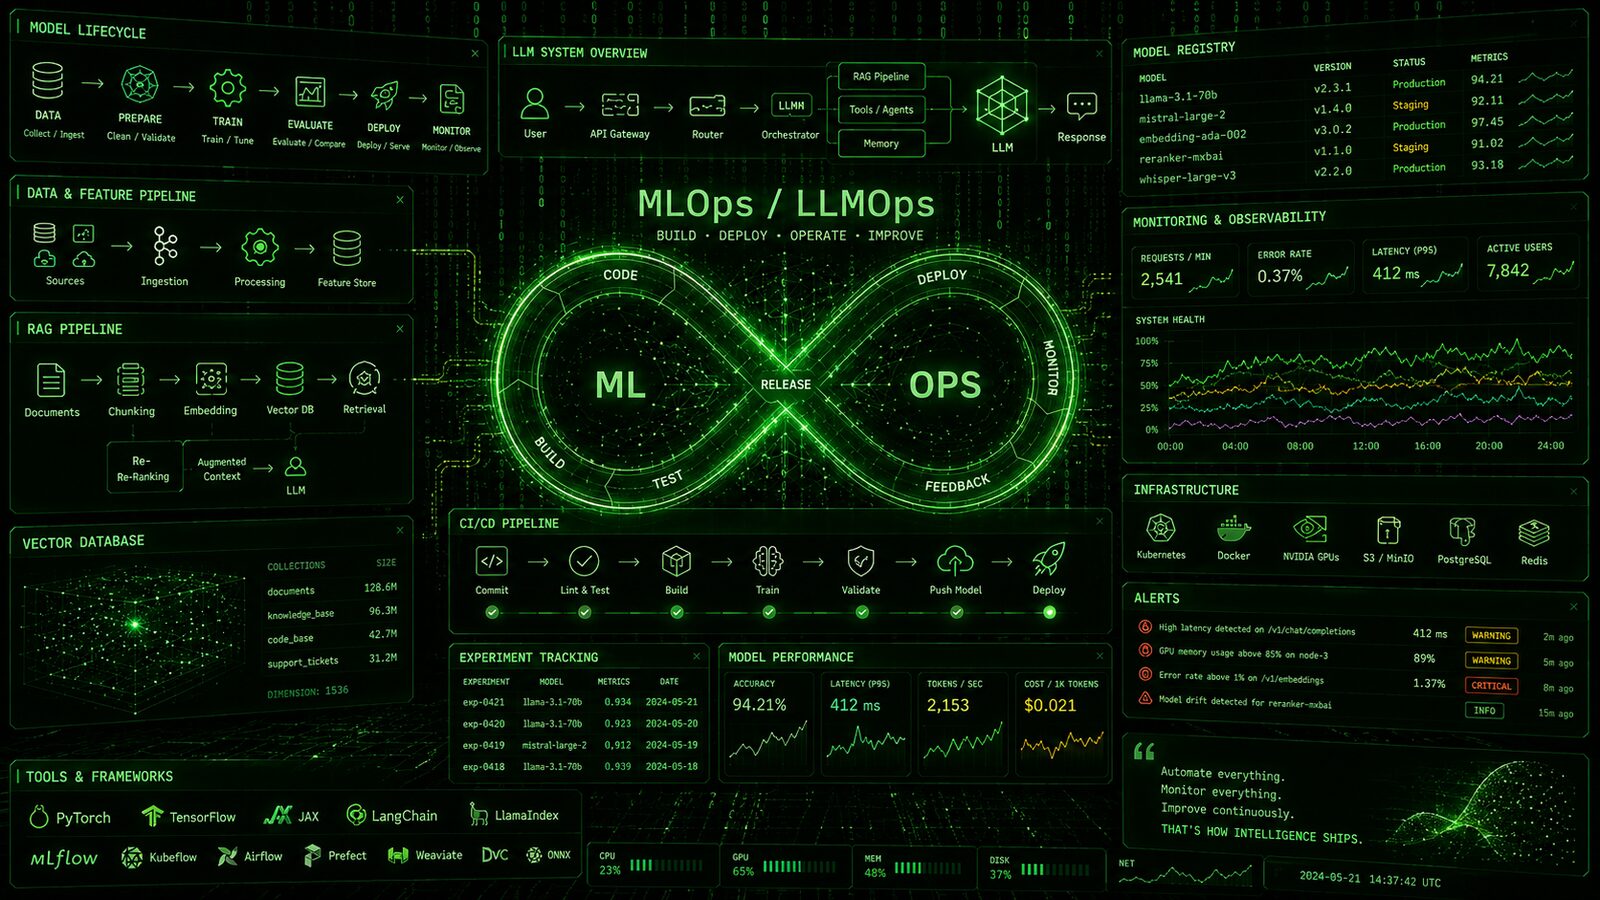
MLOps / LLMOps
MLOps / LLMOps
MLOps / LLMOps

Runs models the same way infra gets run — self-hosted where it makes sense, evaluated, and monitored.

Discover ↗
← Back
MLOps / LLMOps

Runs models the same way infra gets run — self-hosted where it makes sense, evaluated, and monitored.

Self-hosted inference via Ollama, running quantized models locally for cost and privacy
Deliberate routing between local and hosted models based on task sensitivity and latency
Embedding pipelines and vector search for local knowledge retrieval
Evaluates models on real tasks before trusting them in a workflow, not just benchmarks
Self-hosted inference (Ollama) Model selection & quantization Embeddings & vector search Local + hosted model routing Eval-driven iteration Latency/cost tradeoffs
EE S09
Offensive Security
Offensive Security
Offensive Security

Authorized web app pentesting across checkout/payment, XSS, IDOR, account security and the full infrastructure lifecycle, tested against each platform's own known CVE history, not generic scanning.

Discover ↗
← Back
Offensive Security

Authorized web app pentesting across checkout/payment, XSS, IDOR, account security and the full infrastructure lifecycle, tested against each platform's own known CVE history, not generic scanning.

Full authorized engagements end to end: scope and rules of engagement agreed in writing, systematic coverage of the attack surface, written report delivered and reviewed line by line with the owner
Identifies the underlying platform from its own telemetry and tests directly against its known CVE history rather than generic fuzzing
XSS tested across multiple separate rendering surfaces, IDOR across every resource type, account security and session management, file-upload handling
Root-cause investigation under live engagement conditions — traces a symptom back through logs and system state to the real mechanism, not just the first plausible explanation
Working a structured certification path: Security+ → CySA+ → GCFE/GCFA
Authorized Web App Pentesting XSS IDOR Auth/Session Testing CVE Research Price/Parameter Tampering
EE E01
Assistant Manager & IT Infrastructure Lead

Terra Europa Hotel — BRONTES BC — Targovishte, Bulgaria
Oct 2021 – Present

Discover ↗
← Back
Assistant Manager & IT Infrastructure Lead

Terra Europa Hotel — BRONTES BC — Targovishte, Bulgaria
Oct 2021 – Present

Full hotel network design & deployment. Proxmox virtualisation. Full-stack hospitality platform (ARK/ks.vg). Mixed OS environment. Level 1–3 support across all departments.

EE E02
Freelance IT Support & Various Roles

Self-employed — United Kingdom
2007 – 2021

Discover ↗
← Back
Freelance IT Support & Various Roles

Self-employed — United Kingdom
2007 – 2021

Freelance PC repair and computer troubleshooting for private clients, alongside non-IT work (driving, delivery, taxi) in the UK.

EE E03
Expert IT Services — ARGE / IT Specialist

Synovate Global Market Research — Istanbul, Turkey
2006 – 2007

Discover ↗
← Back
Expert IT Services — ARGE / IT Specialist

Synovate Global Market Research — Istanbul, Turkey
2006 – 2007

Large-scale server infrastructure for global market research. Server hardware, OS administration, data integrity, internal network support.

EE E04
Expert IT Services Specialist

TEN Underwear — Istanbul, Turkey
2005 – 2006

Discover ↗
← Back
Expert IT Services Specialist

TEN Underwear — Istanbul, Turkey
2005 – 2006

Expert-level IT support across Windows and Linux in manufacturing & retail environments.

EE E05
IT Services & Web Design Specialist

Locomotif IT Services — Istanbul, Turkey
2002 – 2004

Discover ↗
← Back
IT Services & Web Design Specialist

Locomotif IT Services — Istanbul, Turkey
2002 – 2004

IT services, web design, and project delivery. Dreamweaver, Fireworks, Flash, Photoshop.

EE E06
Technical Specialist & IT Support

Kale / DMS / Anet Communication — Istanbul, Turkey
1997 – 2001

Discover ↗
← Back
Technical Specialist & IT Support

Kale / DMS / Anet Communication — Istanbul, Turkey
1997 – 2001

Hardware diagnosis, repair, assembly. ISP first-line support during the formative period of consumer internet in Turkey.

About
Emil Emilov
Infrastructure specialist · Network & Security Engineer

I build and secure the infrastructure other things run on — networks, virtualization, and the systems in between. 25+ years across networking, security, and DevOps: freelance PC repair and IT support for private clients in the UK, then running the full network and hospitality platform for a live hotel property in Bulgaria since 2021, alongside a homelab that mirrors production practice at small scale — VLANs, failover routing, containerized services, backups that actually get tested.

Open to full-time roles in Network Engineering, Security, or DevOps/Infrastructure — remote or EU relocation.

Capabilities
Networking
Security
Virtualisation
Storage
Operating Systems
Development
AI Engineering
MLOps / LLMOps
Offensive Security